


SAS PCE for Stormshield SNS
Thales protects a wide range of enterprise resources, including network access through Stormshield SNS appliances. The Stormshield SNS integration with SafeNet Access Exchange (SAE) extends identity protection to captive portal and SSL VPN access by supporting OpenID Connect (OIDC) authentication and multi-factor authentication (MFA).
In this integration, Stormshield SNS communicates with SafeNet Access Exchange through OIDC to authenticate users requesting network access. SafeNet Access Exchange provides centralized identity management and authentication, enabling single sign-on (SSO) for subsequent access through the captive portal and SSL VPN.
The integration comprises the following components:
- SafeNet Access Exchange (SAE): It is an on-premises identity provider (IDP), which complements with secure authentication of Stormshield SNS.
- Stormshield SNS: Provides network access control through captive portal and SSL VPN, acting as an OpenID Connect relying party.
Supported Use Cases
This integration supports the following use cases:
- Stormshield Captive Portal login: Users authenticate through the Stormshield Captive Portal using OIDC-based multi-factor authentication provided by SafeNet Access Exchange.
- Stormshield SSL VPN client login: Users authenticate through the SSL VPN client using OIDC-based multi-factor authentication provided by SafeNet Access Exchange.
- Stormshield SNS admin console authentication: Administrators authenticate to the Stormshield SNS administration console using centralized identity verification through SafeNet Access Exchange.
Authentication Flow
The image below illustrates the authentication process, which ensures secure access to Stormshield SNS network resources.
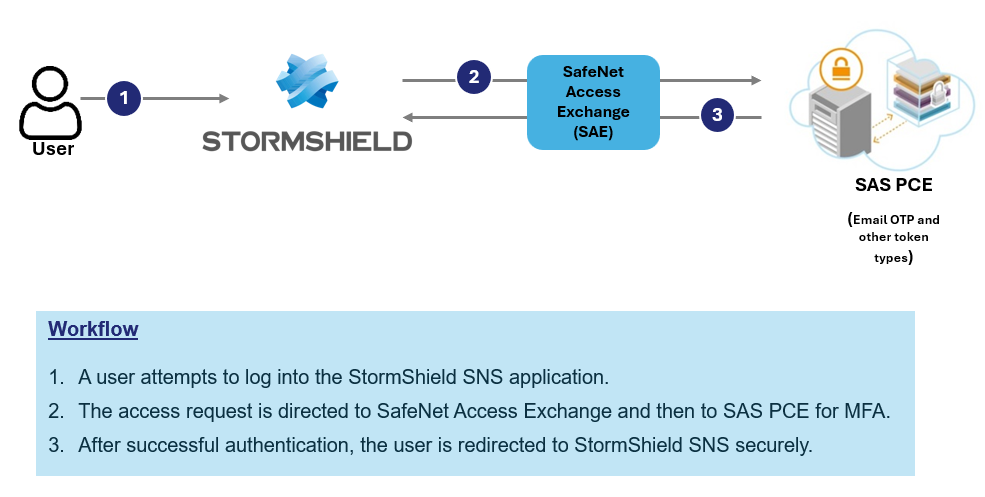
Integrate SafeNet Access Exchange with Stormshield SNS
Integrating SafeNet Access Exchange with Stormshield SNS is a four-step process:

